Shipped01
3,615
checks on every scan, plus 457 secret patterns
A week of audit work, done in ninety seconds.
BeforeSecurity audit: two weeks, €6,000, and a PDF
AfterFull report in ninety seconds, on every change
Next.jsClaudePrisma
Case · 01
PlatformSecurity scanner for code
Bryxe Shield
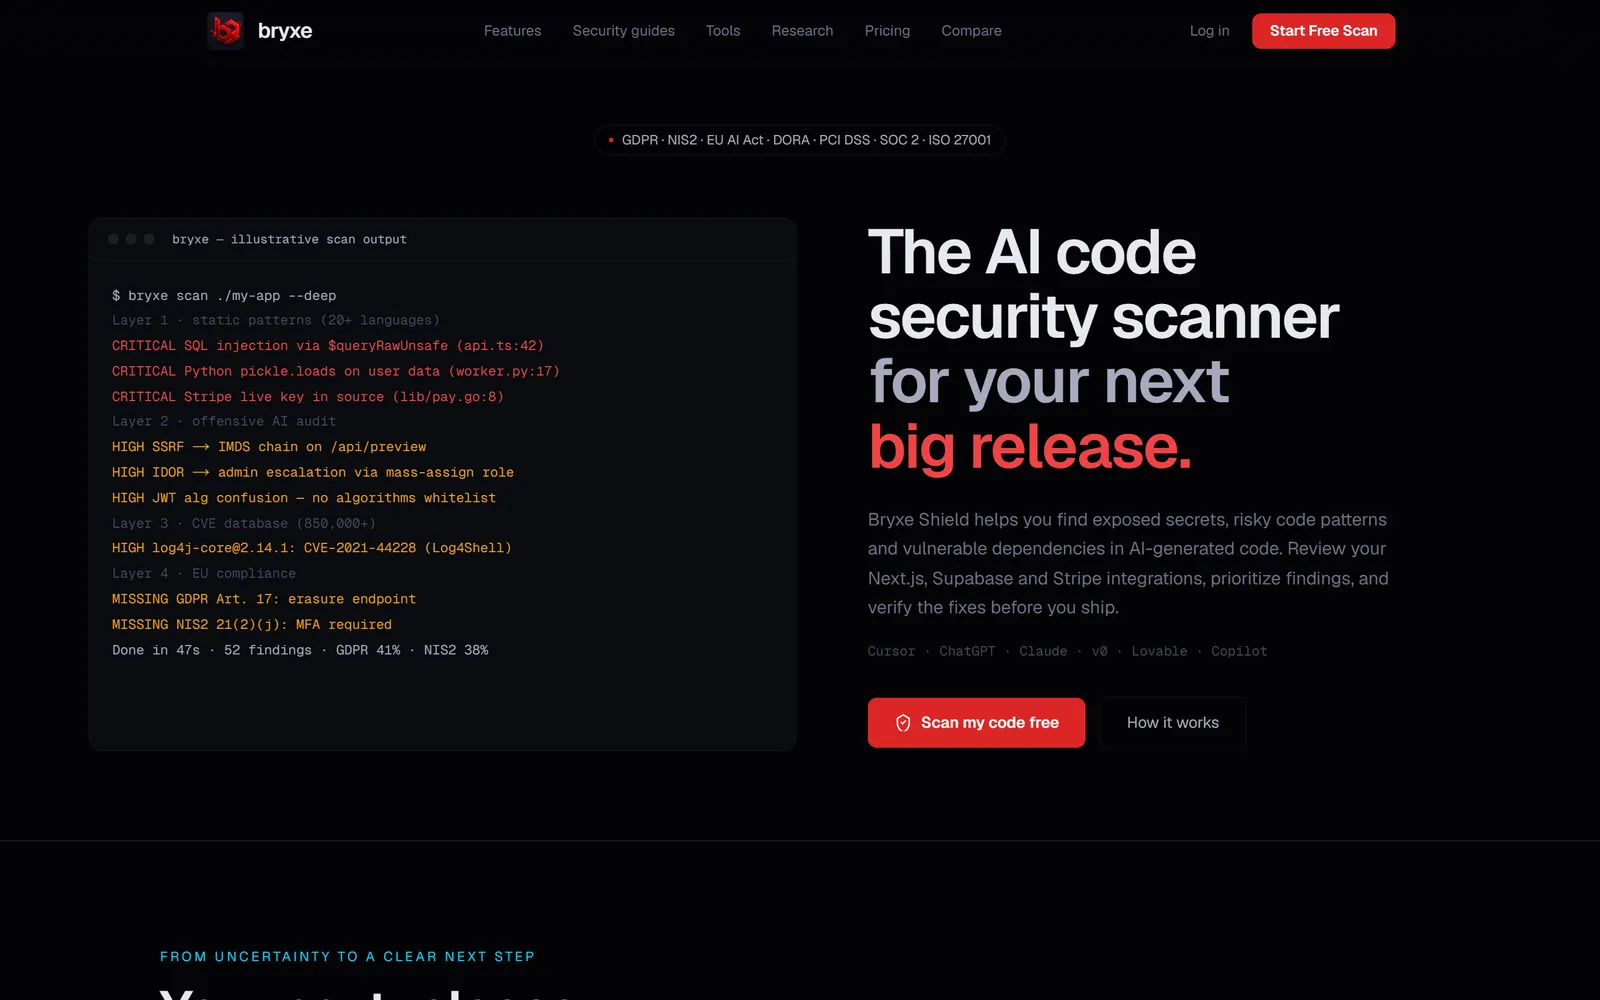
Upload your project and it finds what a security auditor would — leaked passwords, ways in for attackers, outdated parts with known holes. The report is ready to hand to a client or a regulator.
- Explains every hole twice: for the engineer and the owner
- A chat that knows your code and your findings
- A bot sits in GitHub and checks every push
- A security badge for your site and a PDF for the auditor